SBI Data Breach: 3,897 Customer Records Exposed on Dark Web, Probe Launched
The country’s largest public sector bank says core operations remain unaffected as an independent cybersecurity agency investigates the exposure of sensitive customer information
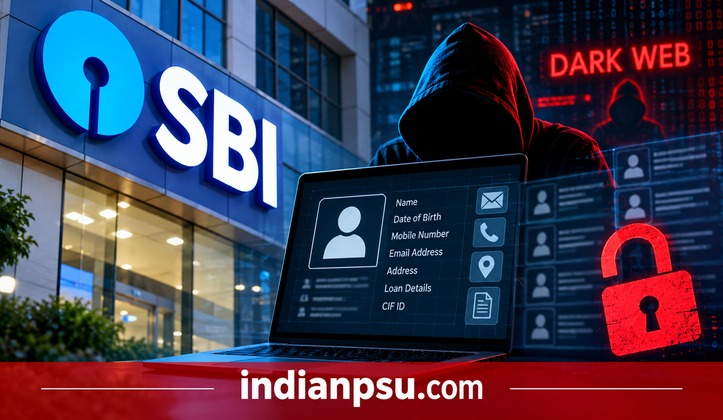
The State Bank of India (SBI) has reported a cybersecurity incident involving the exposure of 3,897 customer records containing personally identifiable information on the dark web, raising fresh concerns over the protection of sensitive banking data.
In a disclosure dated October 21, 2026, SBI said it had received alerts about the suspected exposure on October 16 from the Defence Cyber Agency, the Indian Computer Emergency Response Team (CERT-In) and its threat intelligence service provider.
A preliminary examination of approximately 3.75 lakh records found on the dark web identified 3,897 records containing personally identifiable information, according to the information disclosed by the bank.
Names, Mobile Numbers and Addresses Among Exposed Data
The exposed information reportedly includes customers’ names, dates of birth, gender, registered mobile numbers, email addresses and residential addresses.
The records also contained branch identifiers, Customer Information File (CIF) identifiers, lead IDs and metadata associated with loan records.
The exposure of such information could put affected customers at risk of targeted phishing attempts, fraudulent calls and identity-related misuse. Criminals can use personal and loan-related information to make fraudulent communications appear credible.
The precise origin of the exposure, the circumstances in which the information became accessible and the full extent of the incident remain under investigation.
SBI Appoints Independent Cybersecurity Agency
SBI has activated its cyber incident response and containment procedures and appointed an independent cybersecurity agency empanelled with CERT-In to conduct a forensic investigation.
The investigation is expected to examine the authenticity of the exposed records, establish the source of the leak and determine the full scope of the incident.
The bank has maintained that the incident is not expected to have any material impact on its core business operations, financial performance or business continuity. Its core banking systems continue to operate normally.
However, the final findings of the forensic investigation will be important in determining how the exposure occurred and whether additional remedial measures are required.
Cybersecurity Under Scrutiny in Banking Sector
The incident highlights the growing challenge of protecting customer information as financial institutions face increasingly sophisticated cyber threats.
For banks handling millions of customer relationships, data security extends beyond the protection of account balances and transaction systems. Personal information, customer identifiers and loan-related records can also be exploited for fraud, impersonation and social engineering.
The immediate priority for SBI will be to establish the source and extent of the exposure, strengthen safeguards wherever necessary and address any risks faced by affected customers.
The outcome of the investigation and any subsequent regulatory developments will be closely watched as the case progresses.